TL;DR

Get wellness gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
A November 2 report by Chalmovsky says Ubuntu had not issued a fix for CVE-2026-98432, a Linux kernel TCP vulnerability rated CVSS 9.8, while supported Ubuntu releases were listed as vulnerable. The author says Debian and other distributions had shipped fixes and that they took their Ubuntu servers offline; the provided material does not independently verify the vulnerability details or Ubuntu’s patch status.
A report published November 2 says supported Ubuntu releases remained vulnerable to CVE-2026-98432, a Linux kernel TCP flaw rated CVSS 9.8, more than two weeks after Debian reportedly released a fix. The author, writing on chalmovsky.com, says they took their Ubuntu servers offline after losing confidence in the distribution; the supplied source does not include a response from Canonical or independent confirmation of the patch status.
The report describes CVE-2026-98432 as a critical vulnerability in the Linux kernel’s TCP code that has existed since 2016 and can be attacked remotely. It attributes to Anthropic the claim that a working exploit can obtain root access to a server. The material provides no technical advisory, exploit details, or direct statement from Anthropic, so those points remain claims in the original report rather than independently established here.
According to the author, Debian patched the flaw on October 16, while Ubuntu’s supported releases, including its long-term-support versions, were still marked “Vulnerable” on November 2. The author says the vulnerability had received its 9.8 rating nine days before the post and that the exploit was reported six days before it. The report does not identify the specific Ubuntu releases checked or link to their individual security notices.
The author says they took all their Ubuntu servers offline while considering a migration, because they did not have time to move the services and data immediately. They also state that Debian, Arch and Alpine had shipped fixes. Those distribution comparisons are reported by the author; the supplied material contains no notices from the projects to verify the release dates or package status.
Why Server Operators Are Concerned
If the report’s account is accurate, the gap between a critical rating, a working remote exploit and an available Ubuntu fix could leave administrators of affected systems facing a difficult choice: continue running potentially vulnerable servers, apply a workaround, or interrupt services. The claimed ability to obtain root access would make the issue particularly serious, since that level of access can give an attacker broad control over a system.
The story also matters to organizations that select Ubuntu for long-term support and security maintenance. Administrators need clear information about which releases are affected, whether mitigations are available and when updated packages can be installed. The report raises questions about those matters, but one post and the material supplied here do not establish the scope of exposure across Ubuntu systems or the reasons for any delay.
Taking servers offline, as the author says they did, avoids continued operation but can disrupt services and does not itself resolve the underlying software issue. Readers managing Ubuntu machines should rely on official Ubuntu security notices and their own vulnerability-management procedures rather than treating the author’s account as a substitute for a system-specific assessment.
Products Worth Considering

Levoit Vital 100S-P Air Purifier with Washable Pre-Filter
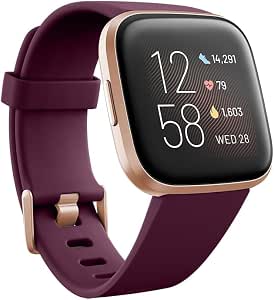
Fitbit Versa 2 Health and Fitness Smartwatch with Heart Rate, Alexa, Music, Sleep and Swim Tracking

BowFlex Results Series SelectTech Adjustable Dumbbells (Pair)
As an affiliate, we earn on qualifying purchases.
The Report’s Patch Timeline
The author’s account sets out a short sequence: the Linux kernel vulnerability is described as dating to 2016; Debian reportedly released a patch on October 16, 2026; and the author says a working exploit and the 9.8 rating had been public for six and nine days, respectively, by the time of the post. The article gives its status timestamp as November 2 at 14:48 UTC.
The report contrasts the claimed Ubuntu delay with language on Ubuntu’s website promising “timely patches for critical vulnerabilities.” It also criticizes broader marketing phrases, including “enterprise-grade” and “production grade,” arguing that these assurances are difficult to reconcile with the reported patch status. That is the author’s assessment, not an independent finding about Canonical’s security processes.
Ubuntu is developed by Canonical and is widely used on servers, including through virtual private server providers, according to the author’s account. The source says the author had chosen it as a stable, low-maintenance server operating system. It does not document how common that choice is, how many systems may be affected, or whether Ubuntu had issued a fix or mitigation after the stated timestamp.
“I’m moving all my servers off Ubuntu.”
— Chalmovsky, author of the November 2 report
Ubuntu’s Current Fix Status
The source provides a snapshot dated November 2, 2026, at 14:48 UTC, not a live status update. It does not establish whether Ubuntu released a patch, workaround or advisory after that time, or explain why the author found supported releases marked vulnerable. Canonical’s response is not included.
The report also does not identify the affected kernel package versions, show an official CVE record or provide links to distribution advisories. Its statements about remote exploitability, root access and fixes from Debian, Arch and Alpine are attributed to the author or to Anthropic, but supporting technical material is absent from the supplied source. The number of affected Ubuntu installations and any confirmed attacks are also unknown.
Check Advisories Before Acting
The next concrete development for Ubuntu users is an official security notice or package update specifying the affected releases, fixed kernel versions and any available mitigations. Administrators should check current Ubuntu Security Notices and package repositories, confirm the kernel version running on each system, and follow their organization’s incident-response process. The report alone does not establish what action is appropriate for every installation.
Any decision to take systems offline or migrate them carries service and data risks, as the author’s account illustrates. Operators should weigh those risks against verified, current vendor guidance and consider continuity plans before making changes. The supplied material gives no date for a Canonical response or for a future update from the report’s author.
Key Questions
What is CVE-2026-98432?
The report describes it as a Linux kernel TCP vulnerability rated CVSS 9.8 and says it can be attacked remotely. The supplied material does not include a technical advisory to verify those details.
What does the report say about Ubuntu patches?
It says supported Ubuntu releases, including long-term-support versions, were listed as vulnerable on November 2, 2026, while Debian had reportedly patched the flaw on October 16. The source does not confirm whether Ubuntu issued a fix after its stated timestamp.
Does the report confirm attackers have exploited the flaw?
No. The author attributes to Anthropic the claim that it built a working exploit capable of obtaining root access, but the supplied material does not report confirmed attacks in the wild.
What should Ubuntu server administrators do?
Check current Ubuntu security advisories and package information for the exact release and kernel in use. Follow official guidance and established security procedures; the report does not provide a system-specific fix or mitigation.
Source: chalmovsky.com